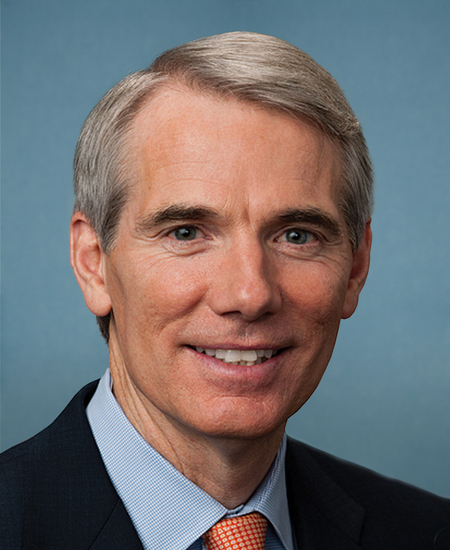
Photo of Rob Portman
R United States Senate · Ohio

Sen. Rob Portman

Compare
Total votes
380
all sessions
Attendance
99%
3 missed
Near the chamber average
With party
83%
of cast votes
Lower than 98% of chamber peers
Bipartisan score
9%
crosses aisle rarely
Higher than 95% of chamber peers
Sponsored
404
bills & resolutions
Near the chamber average
Committees
0
assignments
404 bills and resolutions

Sponsored bills

Total
404
Primary
89
Co-sponsor
315
This page
404
matching current filters
Co-sponsor S 5339
In committee · United States Senate · Co-sponsor
Platform Accountability and Transparency Act

Platform Accountability and Transparency Act This bill increases access to the data of large technology platforms (i.e., platforms with at least 50 million unique monthly users in the United States) in order to facilitate research concerning activities on those platforms, particularly by requiring platforms to disclose data to researchers who participate in a research program jointly established by the National Science Foundation and the Federal Trade Commission.

In committee Dec 21, 2022 1 co-sponsor
Primary S 5311
In committee · United States Senate · Lead sponsor
IRS Customer Service and Transformation Act of 2022

IRS Customer Service and Transformation Act of 2022 This bill requires the Internal Revenue Service (IRS) to submit an initial plan to Congress to address how it intends to meet customer service and technology modernization and related objectives. The IRS must submit semiannual updates to the plan, indicate progress made in implementing the plan, and any changes or challenges in implementing the plan. The bill requires the Government Accountability Office in each calendar year after 2022 and before 2032, to report to specified congressional committees on various matters relating to the IRS, including the progress of the IRS in meeting its objectives and on technology modernization. The bill sets forth customer service objectives that the IRS must accomplish not later than January 1, 2025. It must make available to the public not later than January 1, 2026, certain electronic forms and filing procedures. Finally, the National Taxpayer Advocate is authorized to appoint counsel in the Office of the Taxpayer Advocate to report directly to the National Taxpayer Advocate.

In committee Dec 20, 2022 0 co-sponsors
Primary S 4052
Signed into law · United States Senate · Lead sponsor
Early Hearing Detection and Intervention Act of 2022

Early Hearing Detection and Intervention Act of 2022 This act reauthorizes through FY2027 various activities carried out by the Health Resources and Services Administration, the Centers for Disease Control and Prevention, and the National Institute on Deafness and Other Communication Disorders that support screening and early intervention services for newborns, infants, and young children who are deaf or hard of hearing. The Government Accountability Office must also conduct a study of state early hearing detection and intervention programs, including with respect to disparities in accessing the programs.

Signed into law Dec 20, 2022 0 co-sponsors
Co-sponsor S 3875
Signed into law · United States Senate · Co-sponsor
Community Disaster Resilience Zones Act of 2022

Community Disaster Resilience Zones Act of 2022 This act requires the President to continue to maintain a natural hazard assessment program that develops and maintains publicly available products to show the risk of natural hazards across the United States. Such products shall show the risk of natural hazards and include ratings and data for loss exposure, social vulnerability, community resilience, and any other element determined by the President. The President shall (1) review the underlying methodology of any product that is a natural hazard risk assessment and receive public input on the methodology and data used for the product, and (2) consider including additional data in any product that is a natural disaster hazard risk assessment. Additionally, the President must conduct such reviews to evaluate and update the assessments at least every five years. Using the reviewed assessments, the President must periodically identify and designate community disaster resilience zones (CDRZs), which shall be (1) the 50 census tracts assigned the highest individual hazard risk ratings; and (2) in each state, not less than 1% of census tracts that are assigned a high individual risk rating, taking into consideration specified geographic balance. The President may provide financial, technical, or other assistance to an eligible entity (a state, Indian tribal government, or local government) that plans to perform a resilience or mitigation project within, or that primarily benefits, a CDRZ.


Signed into law Dec 20, 2022 1 co-sponsor
Co-sponsor S 3499
Signed into law · United States Senate · Co-sponsor
A bill to amend the Post-Katrina Emergency Management Reform Act of 2006 to repeal certain obsolete requirements, and for other purposes.

This act repeals a provision of the Post-Katrina Emergency Management Reform Act of 2006 that requires the Department of Homeland Security to promulgate regulations to minimize the excessive use by contractors of subcontractors or tiers of subcontractors to perform the principal work of any contract for facilitating response to or recovery from a natural or man-made disaster.

Signed into law Dec 20, 2022 1 co-sponsor
Co-sponsor S 5298
In committee · United States Senate · Co-sponsor
A bill to provide the Under Secretary for Science and Technology of the Department of Homeland Security with the authority to temporarily extend the duration of protections provided under the SAFETY Act, and for other purposes.

This bill authorizes the Science and Technology Directorate to extend, during FY2023 and under certain circumstances, liability protections that apply if qualified anti-terrorism technologies are deployed in defense against, in response to, or for recovery from an act of terrorism.

In committee Dec 19, 2022 1 co-sponsor
Co-sponsor S 4913
In committee · United States Senate · Co-sponsor
Securing Open Source Software Act of 2022

Securing Open Source Software Act of 2022 This bill sets forth the duties of the Cybersecurity and Infrastructure Security Agency (CISA) regarding open source software security. Open source software means software for which the human-readable source code is made available to the public for use, study, re-use, modification, enhancement, and re-distribution. Specifically, CISA must perform outreach and engagement to bolster the security of open source software; support federal efforts to strengthen the security of such software; coordinate with nonfederal entities on efforts to ensure the long-term security of such software; serve as a public point of contact regarding the security of such software for nonfederal entities; and support federal and nonfederal supply chain security efforts by encouraging efforts to bolster open source software security. CISA must (1) publicly publish a framework, incorporating government, industry, and open source software community frameworks and best practices, for assessing the risk of open source software components; and (2) update the framework at least annually. The bill provides for a critical infrastructure assessment study and pilot assessment. CISA's Cybersecurity Advisory Committee may establish a software security subcommittee, including open source software security. The Office of Management and Budget, in coordination with CISA, the Office of the National Cyber Director, and the General Services Administration, shall issue guidance on the responsibilities of the chief information officers at specified agencies regarding open source software.

In committee Dec 19, 2022 1 co-sponsor
Co-sponsor S 4687
In committee · United States Senate · Co-sponsor
Safeguarding the Homeland from the Threats Posed by Unmanned Aircraft Systems Act of 2022

Safeguarding the Homeland from the Threats Posed by Unmanned Aircraft Systems Act of 2022 This bill provides statutory authority for the Department of Homeland Security (DHS) and the Department of Justice (DOJ) to authorize their personnel to act to detect, identify, monitor, track, and mitigate a credible threat that an unmanned aircraft system (i.e., drone) poses to the safety or security of certain facilities or assets. For example, DHS and DOJ may carry out a pilot program to evaluate the potential benefits of state, local, tribal, and territorial law enforcement agencies taking actions to mitigate credible unmanned aircraft system threats. Additionally, DHS and DOJ must coordinate with the Federal Aviation Administration before carrying out any action authorized by the bill to ensure the action does not adversely impact or interfere with safe airport operations, navigation, air traffic services, or the safe and efficient operation of the national airspace system.

In committee Dec 19, 2022 1 co-sponsor
Co-sponsor S 4465
In committee · United States Senate · Co-sponsor
Offices of Countering Weapons of Mass Destruction and Health Security Act of 2022

Offices of Countering Weapons of Mass Destruction and Health Security Act of 2022 This bill reauthorizes the Countering Weapons of Mass Destruction (CWMD) office in the Department of Homeland Security (DHS) and provides statutory authority for a new Office of Health Security. The CWMD office shall perform duties to coordinate and guide DHS efforts to counter weapons of mass destruction (WMD) and chemical, biological, radiological, and nuclear and other related emerging threats. The Office of Health Security shall have the responsibility for oversight of all medical, public health, and workforce safety matters of DHS.

In committee Dec 19, 2022 1 co-sponsor
Co-sponsor S 2902
In committee · United States Senate · Co-sponsor
Federal Information Security Modernization Act of 2021

Federal Information Security Modernization Act of 2021 This bill addresses federal information security management, notification and remediation of cybersecurity incidents. For example, the bill requires (1) the Cybersecurity and Infrastructure Security Agency to perform ongoing and continuous assessments of federal information security risk posture; and (2) federal agencies to take certain actions in response to information security breaches, such as notifying affected individuals.

In committee Dec 19, 2022 1 co-sponsor
Showing 11 to 20 of 404 bills