

Healthcare Cybersecurity Act of 2025
HR 3841, the Healthcare Cybersecurity Act of 2025, requires the Cybersecurity and Infrastructure Security Agency (CISA) and the Department of Health and Human Services (HHS) to coordinate on improving cybersecurity for healthcare facilities. It mandates appointing a CISA-HHS liaison, updating a sector-specific risk management plan within one year (including analysis of impacts on rural and small facilities), and creating a biannually updated list of high-risk healthcare assets to prioritize support. The bill also directs CISA to provide training for healthcare providers on cybersecurity risks and mitigation. These provisions directly affect hospitals, clinics, and other healthcare entities handling patient data, aiming to reduce breaches and improve resilience against cyberattacks.
Bill status
in committee
1 of 4 stages cleared
Introduction
Jun 2025
Committee Review
Floor Vote
President
Introduced Jun 9, 2025
Last action Jun 10, 2025
Floor votes
How they voted
No floor votes recorded yet.
Full legislative history
Actions timeline
Total actions
3
Key actions
0
Committee
2
Jun 10, 2025
Committee
Referred to the Subcommittee on Cybersecurity and Infrastructure Protection.
lower
Jun 9, 2025
Committee
Referred to the Committee on Homeland Security, and in addition to the Committee on Energy and Commerce, for a period to be subsequently determined by the Speaker, in each case for consideration of such provisions as fall within the jurisdiction of the committee concerned.
lower
Jun 9, 2025
Introduced
Introduced in House
lower
1 primary · 2 co-sponsors
Sponsors
Role
Legislator
Party
State
District
P
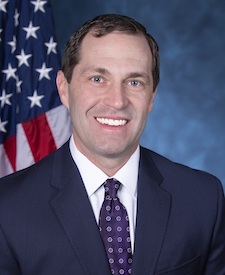
Jason Crow
DDemocratic
Co
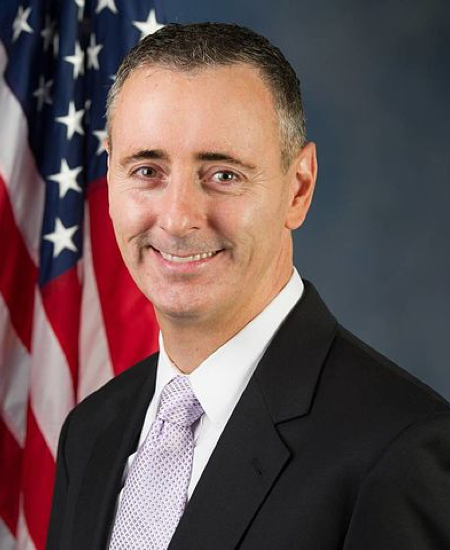
Brian K. Fitzpatrick
RRepublican
Co
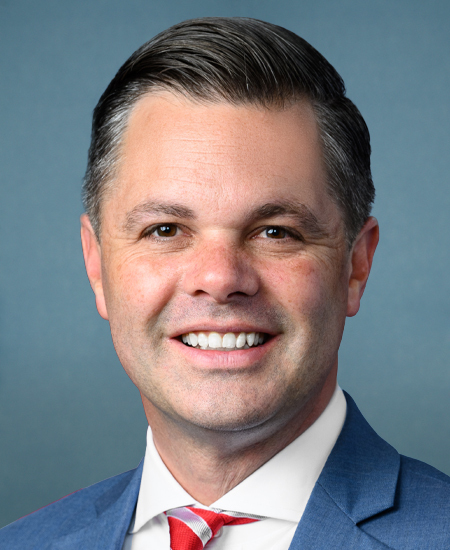
Zachary Nunn
RRepublican
Ask Maddy
·
AI policy assistant
Ask Maddy about HR 3841
Scope: US
Hi! I can help you understand HR 3841. What would you like to know?
Try one of these
i
Maddy answers using official bill text and legislative records. Always verify before sharing.
Sources cited inline