

Securing Open Source Software Act of 2023
The Securing Open Source Software Act of 2023 requires federal agencies to improve the security of open source software, which is widely used in government systems and critical infrastructure. The bill mandates that the Department of Homeland Security develop a framework for assessing security risks in open source software components, conduct regular assessments of software used by federal agencies, and coordinate with the open source community. It establishes pilot programs for federal agencies to create "open source functions" modeled after those in the private sector to manage risks and encourage secure usage. The law affects all covered federal agencies and requires them to report on their efforts to Congress. This represents a concrete policy change that shifts federal responsibility toward securing the open source software ecosystem.
Bill status
in committee
1 of 4 stages cleared
Introduction
Mar 2023
Committee Review
Floor Vote
President
Introduced Mar 22, 2023
Last action May 16, 2023
Floor votes
How they voted
No floor votes recorded yet.
Full legislative history
Actions timeline
Total actions
5
Key actions
2
Committee
3
May 16, 2023
Upper · Passed
Committee on Homeland Security and Governmental Affairs. Reported by Senator Peters with amendments. With written report No. 118-32.
upper
Mar 29, 2023
Upper · Passed
Committee on Homeland Security and Governmental Affairs. Ordered to be reported without amendment favorably.
upper
Mar 22, 2023
Committee
Read twice and referred to the Committee on Homeland Security and Governmental Affairs.
upper
Mar 22, 2023
Introduced
Introduced in Senate
upper
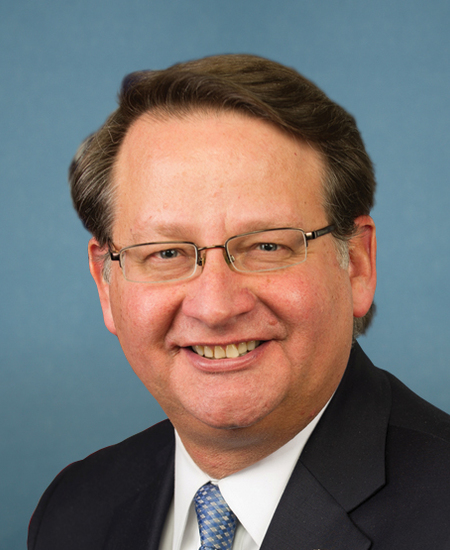
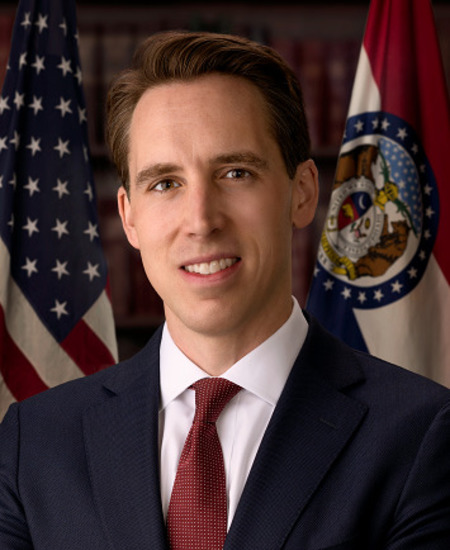
1 primary · 1 co-sponsor
Sponsors
Ask Maddy
·
AI policy assistant
Ask Maddy about S 917
Scope: US
Hi! I can help you understand S 917. What would you like to know?
Try one of these
i
Maddy answers using official bill text and legislative records. Always verify before sharing.
Sources cited inline