

Building Cyber Resilience After SolarWinds Act of 2023
This bill mandates a 120-day investigation by the Cybersecurity and Infrastructure Security Agency (CISA) Director into the impact of the 2020 SolarWinds cyberattack on federal systems and critical infrastructure. It requires a detailed report to Congress on findings, security gaps, and recommendations to improve resilience, including how agencies implemented Executive Order 14028. The bill also directs the Government Accountability Office (GAO) to assess the Cyber Safety Review Board’s effectiveness within one year. The report will address information gaps and suggest ways to close them. This is a procedural measure focused on accountability and learning from a specific past incident, not creating new regulations.
Bill status
in committee
1 of 4 stages cleared
Introduction
May 2023
Committee Review
Floor Vote
President
Introduced May 9, 2023
Last action May 9, 2023
Floor votes
How they voted
No floor votes recorded yet.
Full legislative history
Actions timeline
Total actions
3
Key actions
0
Committee
2
May 9, 2023
House · Referred to committee
Referred to the Subcommittee on Cybersecurity and Infrastructure Protection.
May 9, 2023
House · Referred to committee
Referred to the Committee on Homeland Security, and in addition to the Committee on Oversight and Accountability, for a period to be subsequently determined by the Speaker, in each case for consideration of such provisions as fall within the jurisdiction of the committee concerned.
May 9, 2023
House · Introduced
Introduced in House
1 primary · 0 co-sponsors
Sponsors
Role
Legislator
Party
State
District
P
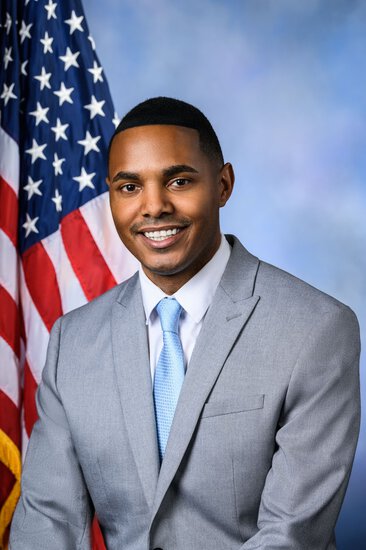
Ritchie Torres
DDemocratic
Ask Maddy
·
AI policy assistant
Ask Maddy about HR 3166
Scope: US
Hi! I can help you understand HR 3166. What would you like to know?
Try one of these
i
Maddy answers using official bill text and legislative records. Always verify before sharing.
Sources cited inline