

Requires businesses in financial, essential infrastructure, and health care industries to develop cybersecurity plans.
This bill requires businesses in New Jersey's financial, essential infrastructure, and healthcare sectors to create and maintain cybersecurity programs. These programs must include risk assessments, incident response plans, and alignment with recognized industry standards like NIST. Businesses must submit their plans to the state's Cybersecurity and Communications Integration Cell (NJCCIC) and annually certify compliance. Non-compliant businesses may face mandatory audits by independent cybersecurity firms at their own expense.
Bill status
in committee
1 of 4 stages cleared
Introduction
Jan 2024
Committee Review
Floor Vote
Governor
Introduced Jan 9, 2024
Last action Jan 9, 2024
Floor votes
How they voted
No floor votes recorded yet.
Full legislative history
Actions timeline
Total actions
1
Key actions
0
Committee
0
Jan 9, 2024
Introduced
Introduced in the Assembly, Referred to Assembly Science, Innovation and Technology Committee
lower
1 primary · 0 co-sponsors
Sponsors
Role
Legislator
Party
State
District
P
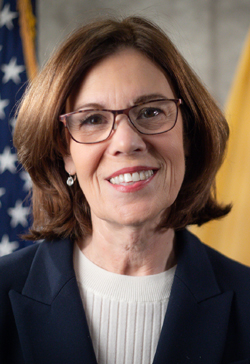
Barbara McCann Stamato
DDemocratic
Ask Maddy
·
AI policy assistant
Ask Maddy about A 2200
Scope: NJ
Hi! I can help you understand A 2200. What would you like to know?
Try one of these
i
Maddy answers using official bill text and legislative records. Always verify before sharing.
Sources cited inline